Threat Trends Digest – September 2026

???

Welcome to the Threat Trends Digest, a monthly view of real-world threat patterns.

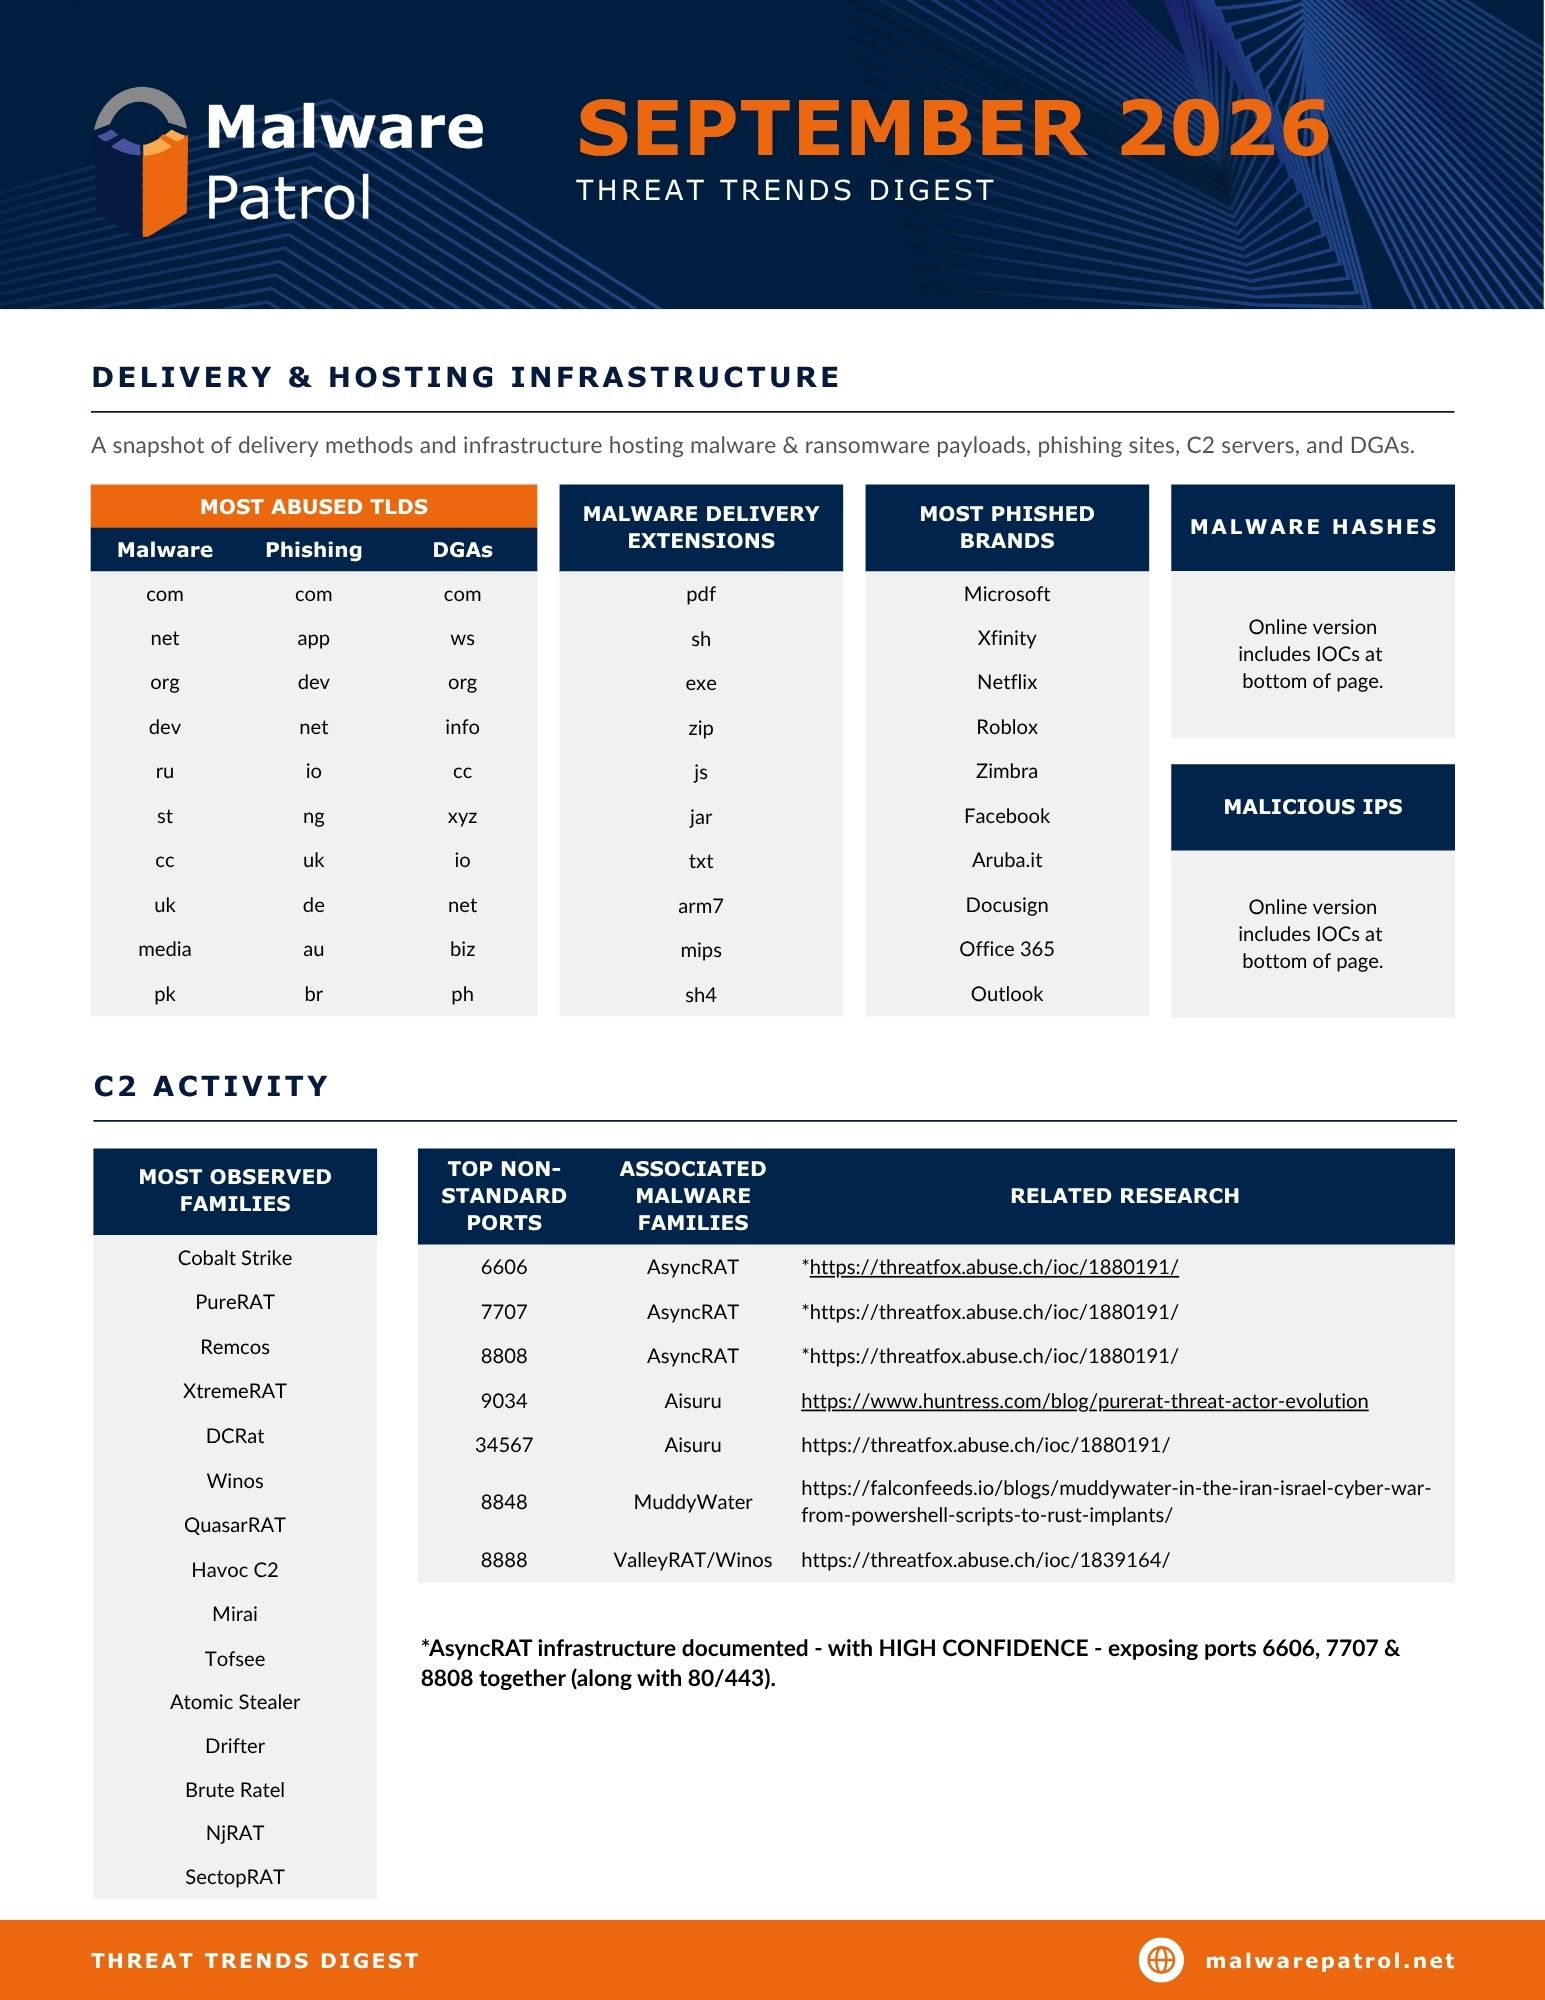
This report compiles data from the previous month using Malware Patrol’s global telemetry and live attack observations to surface key stats on malware, phishing, ransomware, C2s, and domain generation algorithms (DGAs). You’ll find insights into the most exploited TLDs, frequently seen malware hashes and IPs, and other critical indicators. Use this digest to keep a close pulse on attacker behavior, uncover shifting patterns, and better align your defenses with the latest threat activity.

For more articles, check out our #onpatrol4malware blog.
??

IOCs

Malicious IPs

IP Source (ISP/ASN) Country 
106.41.200.151 CHINANET HUNAN PROVINCE NETWORK CN
89.111.158.16 JSC RU-CENTER RU
173.205.127.152 Web Hosting Hub, Inc US
74.115.51.9 Weebly, Inc. US
74.115.51.8 Weebly, Inc. US
185.143.233.238 AbrArvan BGP Anycast IR
185.143.234.238 AbrArvan BGP Anycast IR
43.231.112.25 Apartment # 34, 2nd khoroo MN
162.241.24.119 Unified Layer US
64.40.13.26 GLOBALHOSTINGSOLUTIONS INC US
212.99.45.180 Completel SAS FR
77.65.212.167 PROGRESO.PL SP Z O.O PL
64.37.63.18 HostDime.com, Inc. US
178.48.185.211 2Connect Telecommunications Infrastructure & Network Services Ltd. HU
203.162.31.118 VietNam Data Communication Company VN
213.186.33.19 OVH SAS FR
67.227.189.236 Liquid Web, L.L.C US
213.186.33.4 OVH SAS FR
154.0.169.106 AFRIHOST SP (PTY) LTD ZA
210.245.95.158 FPT Telecom Company VN

Attacking IPs

IP Source (ISP/ASN) Country
193.111.248.174 Ferdinand Zink trading as Tube-Hosting DE
103.161.34.10 GSJZ(CHINA)TECHNOLOGY CO.,LIMITED t/a Guosheng IDC lease DE
176.65.131.18 ZeXoTeK IT-Services GmbH DE
103.161.35.72 GSJZ(CHINA)TECHNOLOGY CO.,LIMITED t/a Guosheng IDC lease DE
193.111.248.216 Ferdinand Zink trading as Tube-Hosting DE
216.152.147.202 GTHost CA
84.247.184.254 Contabo GmbH FR
213.199.50.203 Contabo GmbH FR
192.227.173.60 HostPapa US
103.154.233.221 Netclues Technologies Private Limited IN
213.199.50.230 Contabo GmbH FR
213.199.50.178 Contabo GmbH FR
95.174.113.63 Consumer Internet Cooperative PG-19 RU
104.168.65.101 HostPapa US
45.153.34.104 TechTies Inc. NL
45.153.34.106 TechTies Inc. NL
198.23.197.71 HostPapa US
23.238.92.11 RackNerd LLC US
45.134.226.143 Contabo GmbH FR
146.70.87.165 M247 LTD Los Angeles Infrastructure US

Malware Hashes

Hash VT Detections Classification
eec5c6c219535fba3a0492ea8118b397 53/63 trojan.mirai/mozi
59ce0baba11893f90527fc951ac69912 42/61 trojan.mirai/mozi
31549917cdc6e3f9d40a48ea5998493f 56/67 adware.qjwmonkey/dangeroussig
8bdd2cdd39b2ad7b679faa50f629ce2b 29/62 phishing.akgpp/malurl
3849f30b51a5c49e8d1546960cc206c7 50/62 trojan.mirai/mozi
a73ddd6ec22462db955439f665cad4e6 49/62 trojan.mirai/mozi
796c596185e63803a4ec4003aa60f425 54/68 adware.qjwmonkey/bundler
d4f0c4ab122e0a7f27ba5864934a4ca8 35/64 trojan.sagnt/r002c0db526
dbc520ea1518748fec9fcfcf29755c30 45/62 trojan.mirai/ddos
fbe51695e97a45dc61967dc3241a37dc 47/62 trojan.mirai/mozi
c0fd19c0e4a252efb1864b267fb154ae 53/70 adware.ababsoftware/downloadasist
cbcb58ffe45c202c11bcf2070496aed6 56/67 trojan.cugn/nsis
96dd80012c33291e1621b66f5bd66967 61/69 adware.qjwmonkey/bundler
5116812ebf7d518f7776a1500a26296c 40/64 trojan.mirai/gafgyt
5294f25631d20b68ebf3a9acd4cc1f5d 33/64 trojan.malpack/rootkit
595486a5108206c8bc47b92592b83e28 37/63 trojan.mirai/dirtyfrag
5dfc3eefe1c51312d0020910020c4025 55/67 adware.qjwmonkey/nezchi
0c00a35e30cf2583d06c3a795ee1f0f3 43/71 trojan.webwatcher/occamy
cc354e0cd2cfde3c80a17ead892ea48e 38/63 trojan.mirai/usbli326
afbefb79120fd5d265e6a727825919e8 37/63 trojan.mirai/dirtyfrag

To learn more about how we collect, analyze, and deliver actionable threat intelligence, explore our Threat Intelligence Services. If you’re interested in running your own queries – whether for threat actors, CVEs, infrastructure, or emerging activity – see how our MCP Server helps turn intelligence into practical security insight. Both are designed to support real-world analysis, investigation, and decision-making.

Take advantage of our free threat intel trial.

?

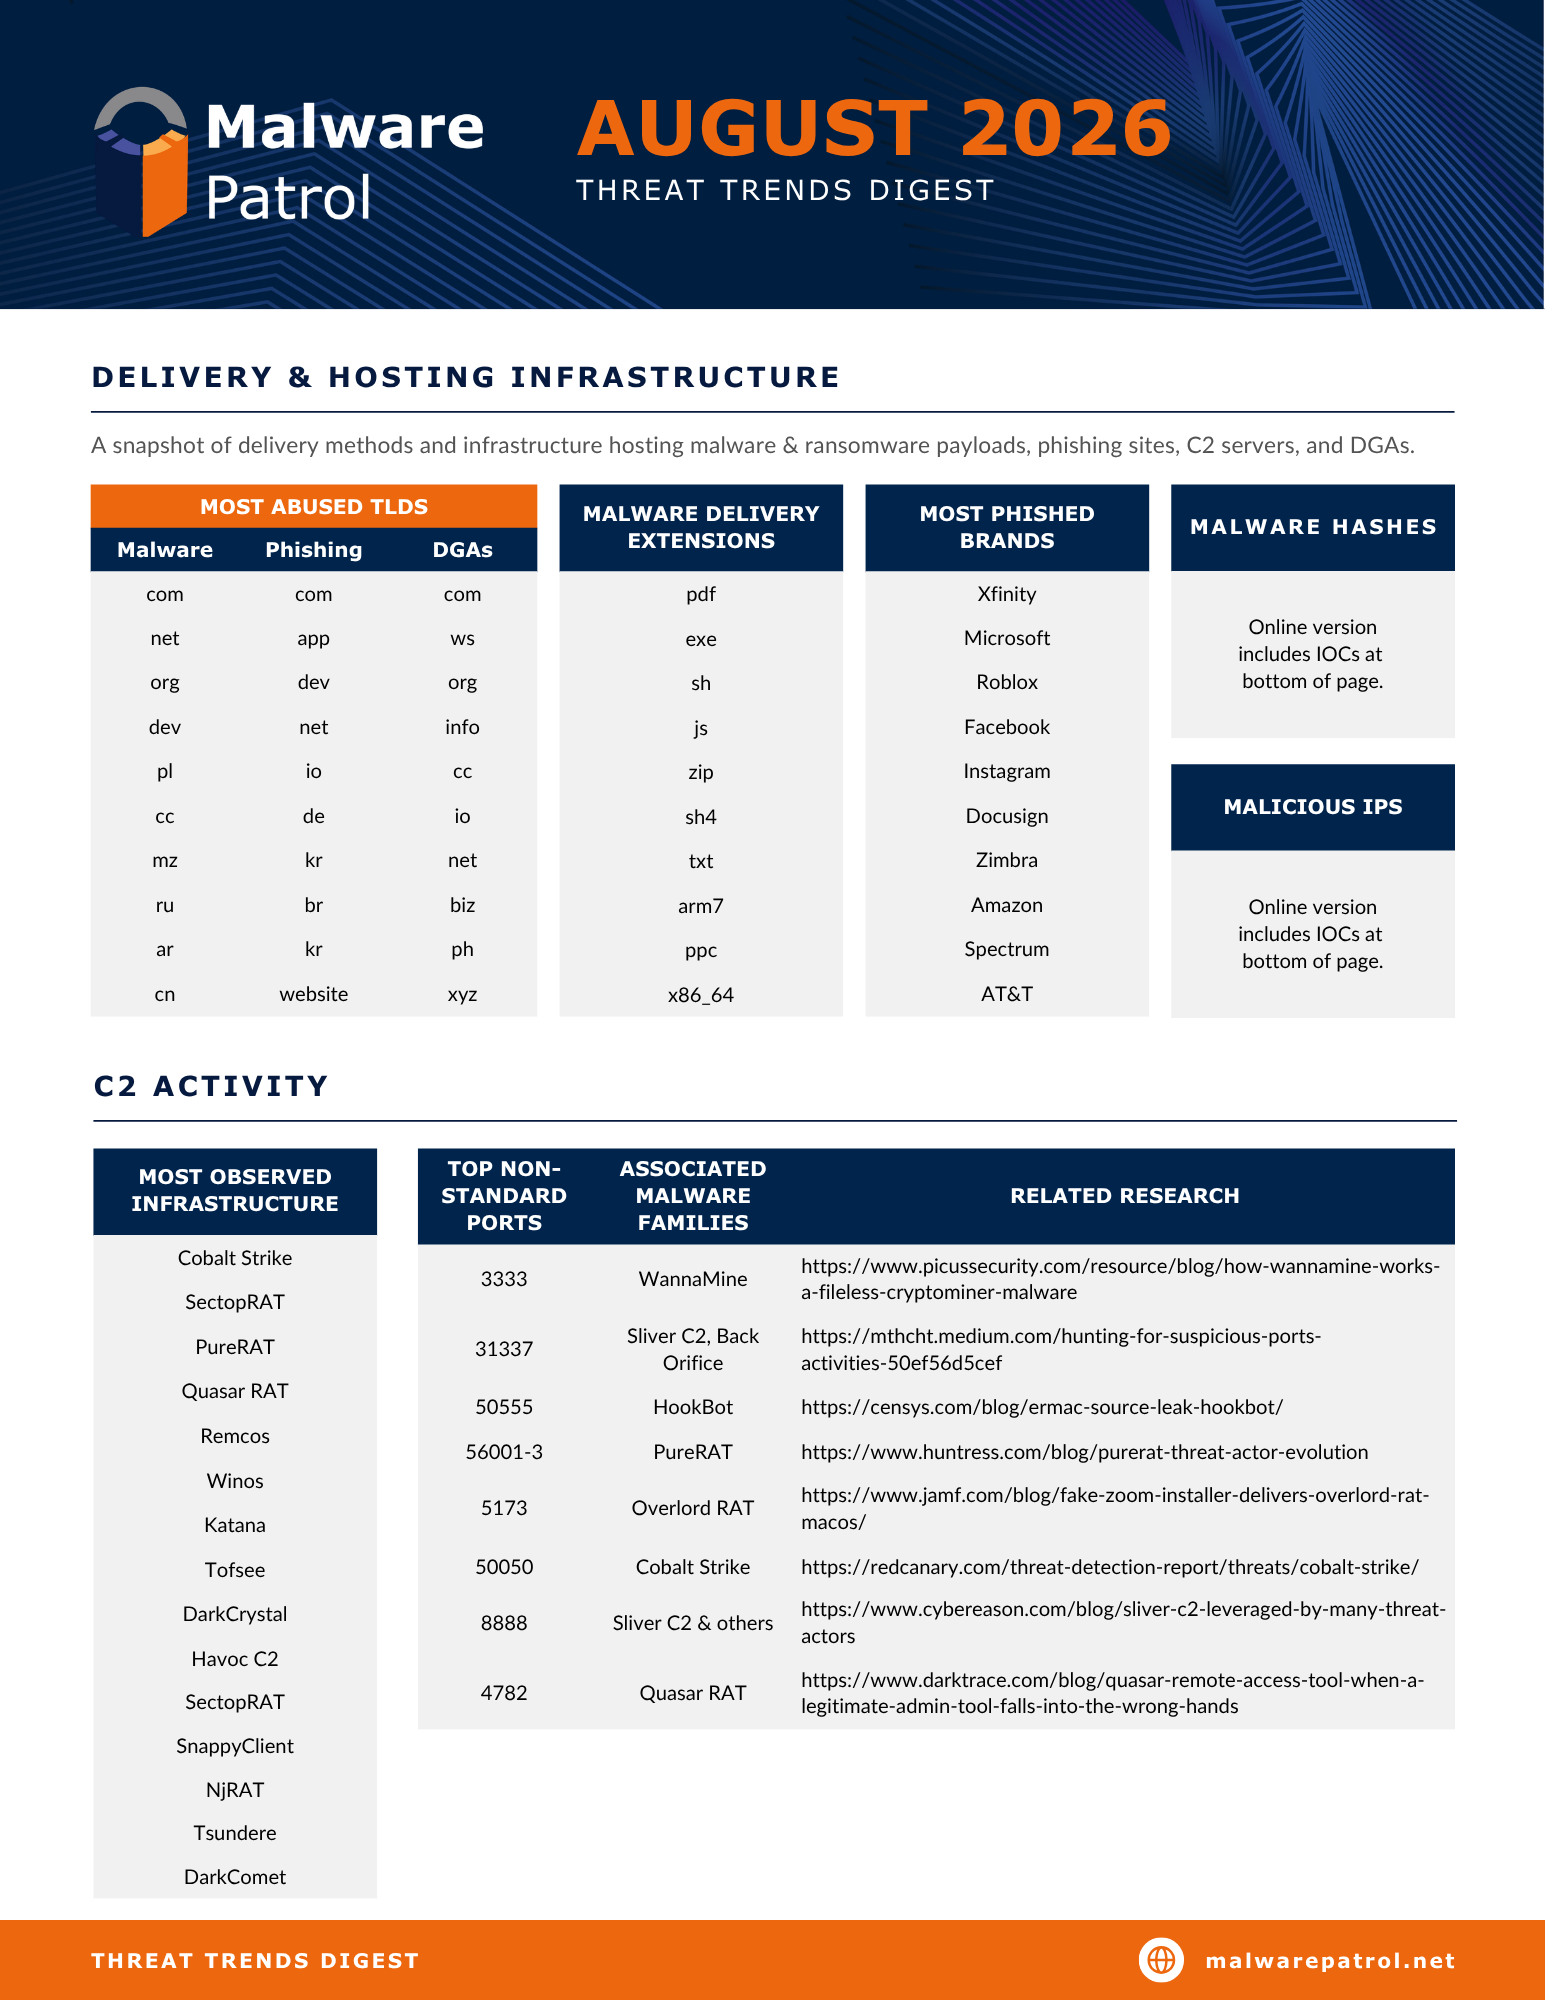
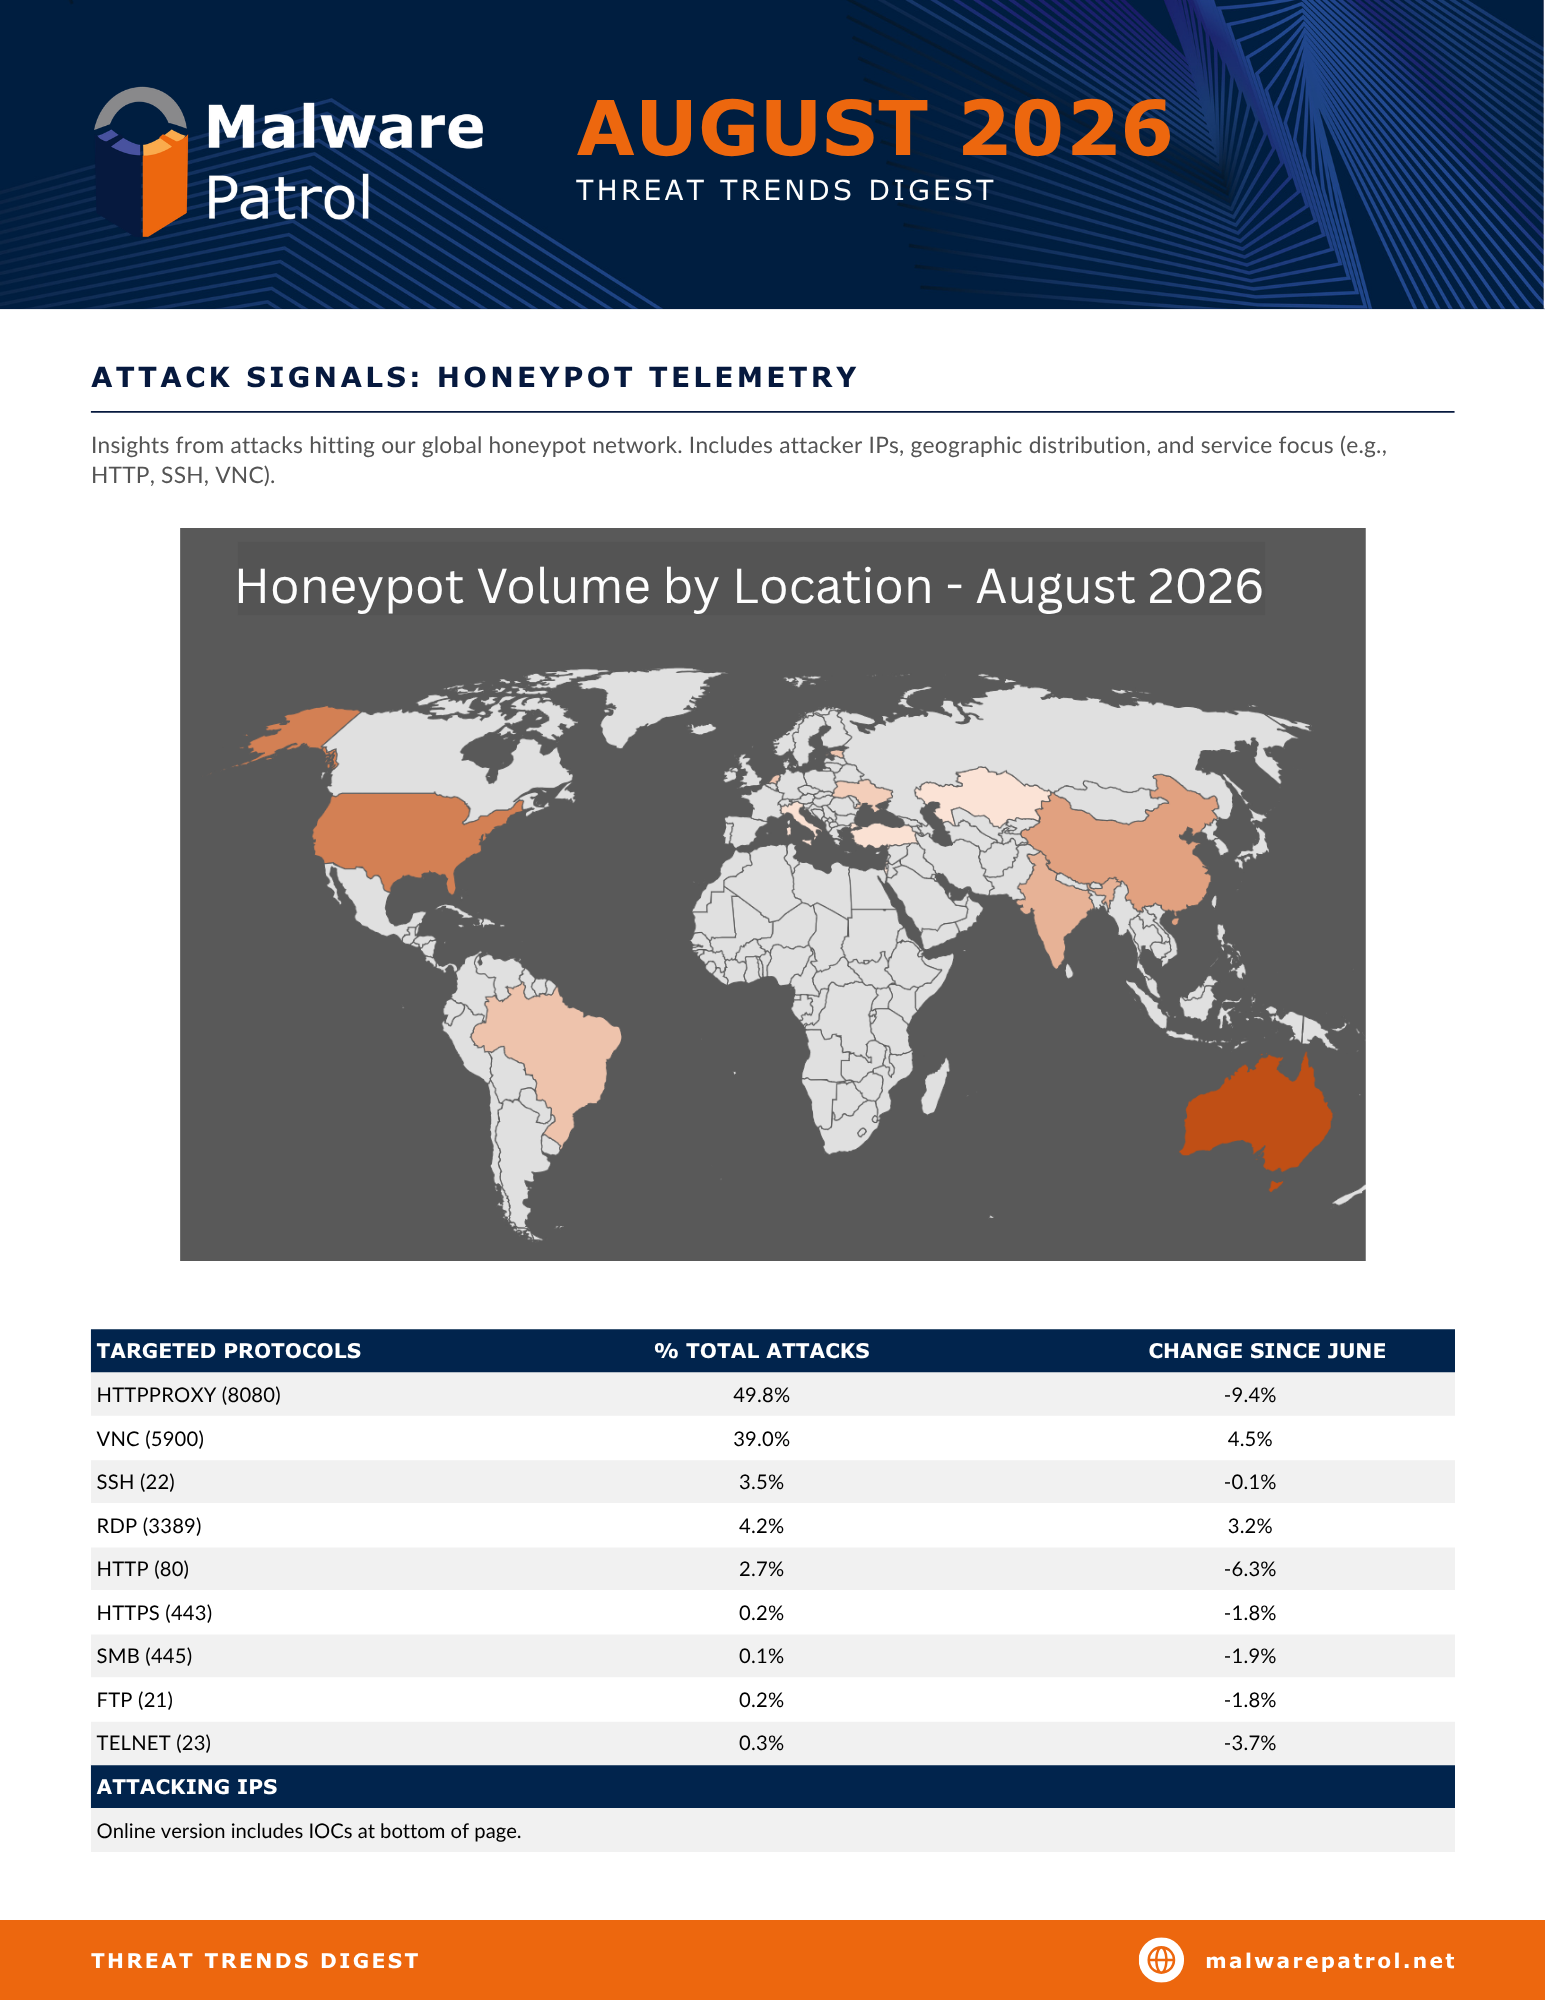
Threat Trends Digest – August 2026

???

Welcome to the Threat Trends Digest, a monthly view of real-world threat patterns.

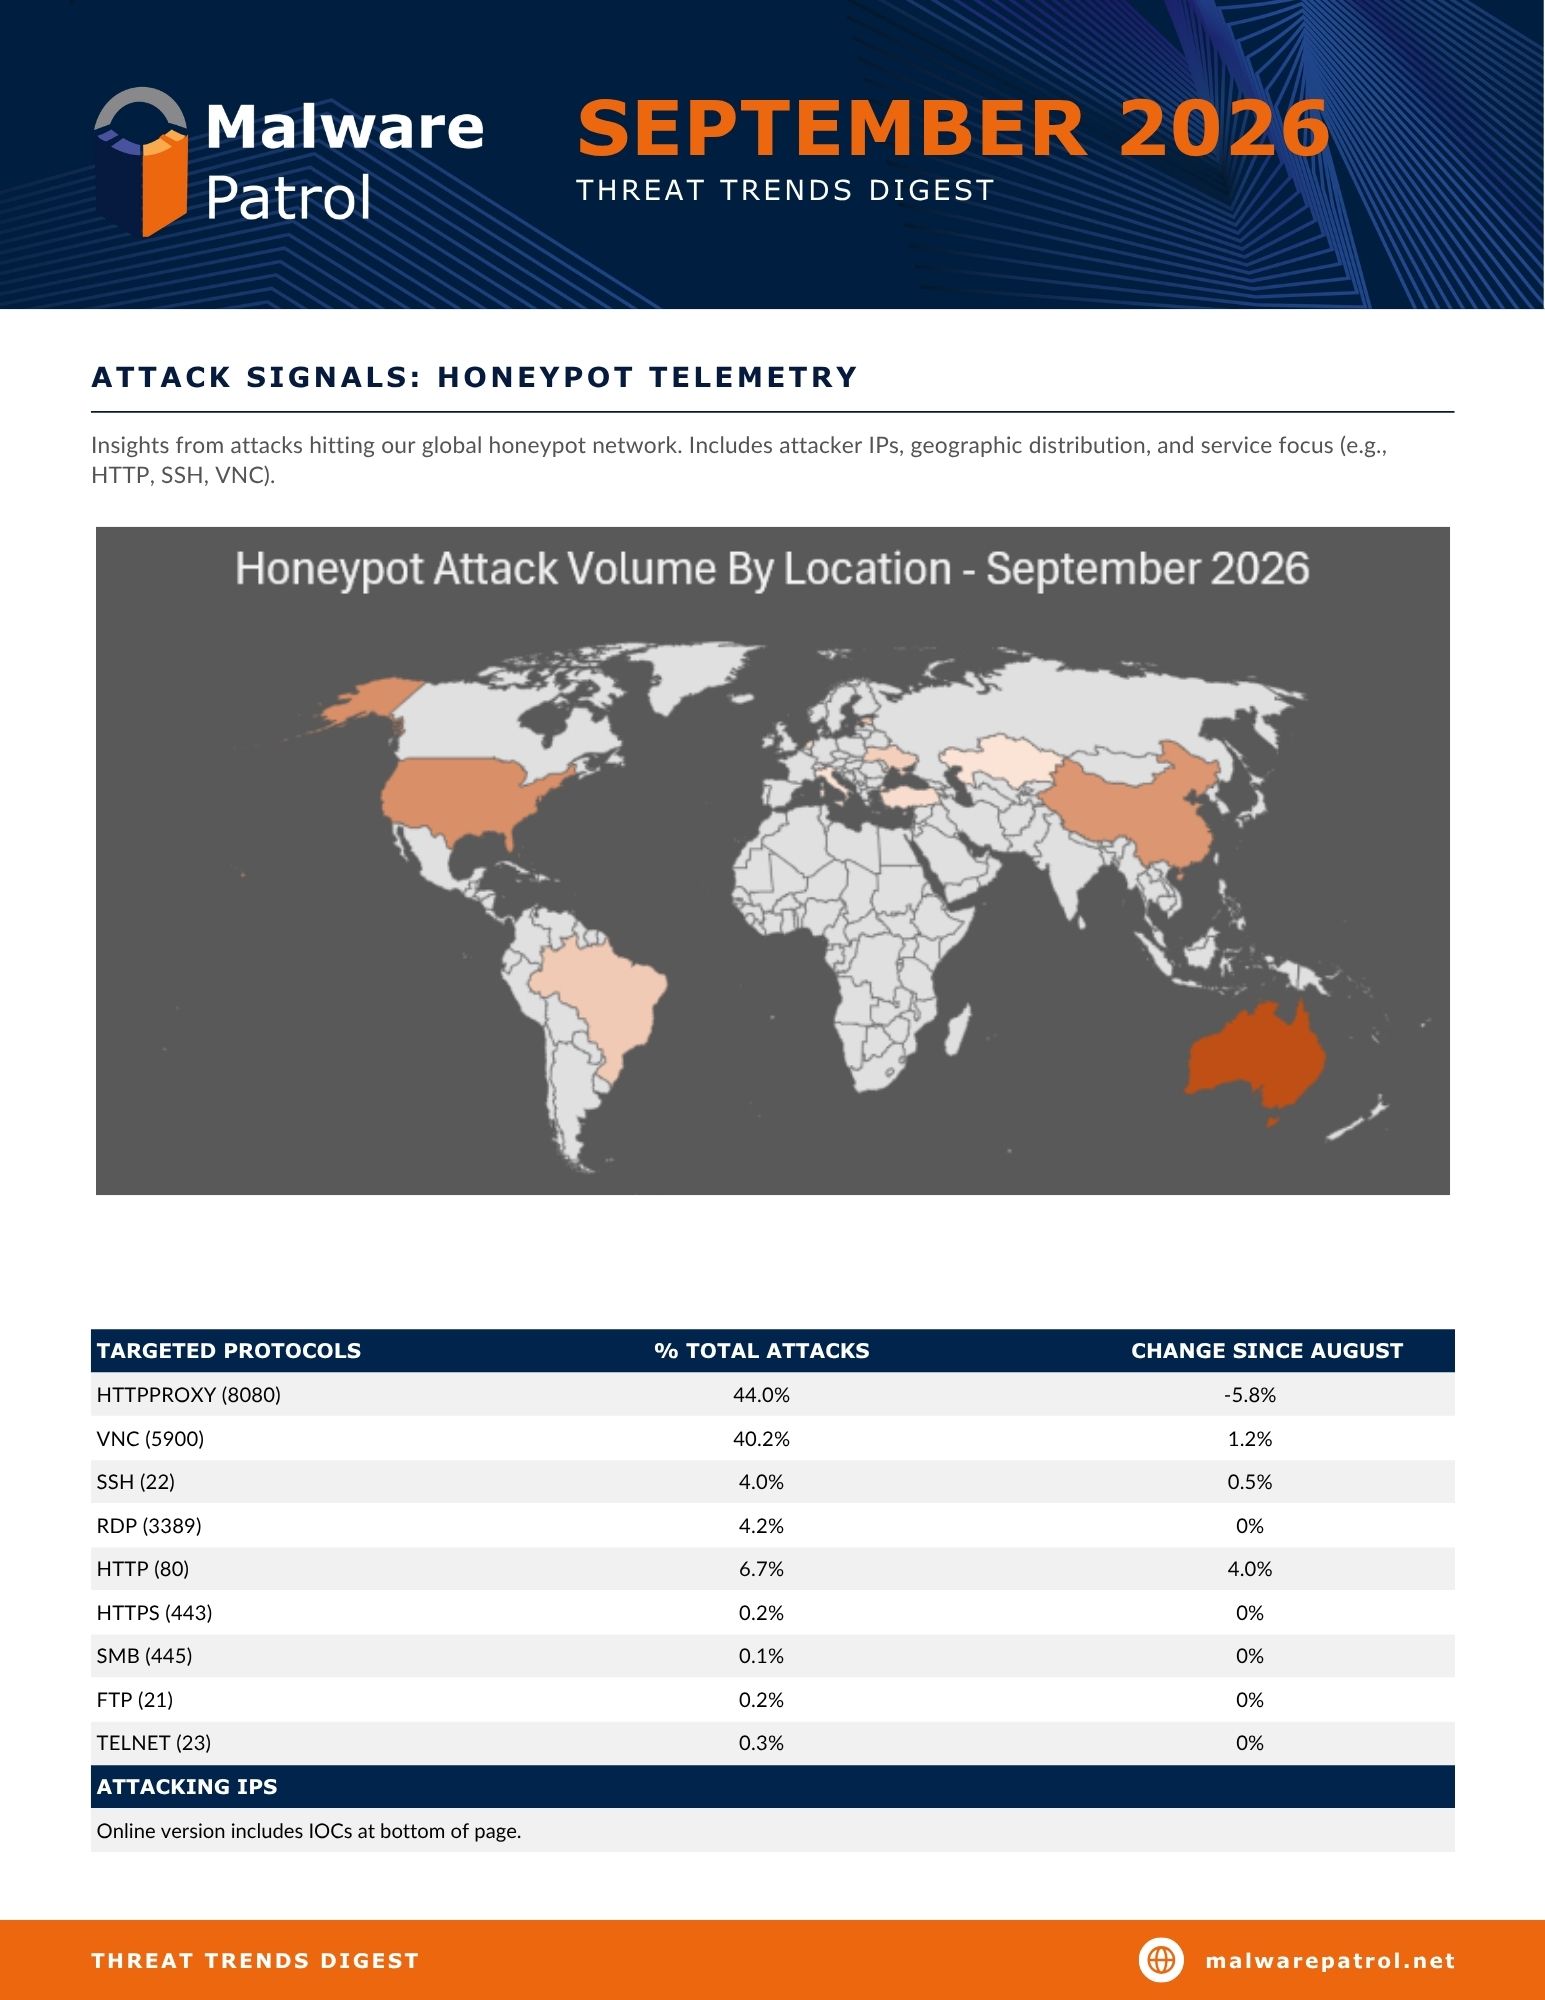
This report compiles data from the previous month using Malware Patrol’s global telemetry and live attack observations to surface key stats on malware, phishing, ransomware, C2s, and domain generation algorithms (DGAs). You’ll find insights into the most exploited TLDs, frequently seen malware hashes and IPs, and other critical indicators. Use this digest to keep a close pulse on attacker behavior, uncover shifting patterns, and better align your defenses with the latest threat activity.

For more articles, check out our #onpatrol4malware blog.
??

IOCs

Malicious IPs


IP Source (ISP/ASN) Country
46.151.182.200 Ghosty Networks LLC LU
188.165.53.185 OVH SAS FR
74.115.51.9 Weebly, Inc. US
213.186.33.87 OVH SAS FR
74.115.51.8 Weebly, Inc. US
5.223.56.39 Hetzner Online GmbH SG
213.186.33.19 OVH SAS FR
64.89.163.215 Meowcore Softworks LLC DE
192.162.199.149 FEMO IT SOLUTIONS LIMITED DE
213.186.33.4 OVH SAS FR
163.44.198.41 GMO INTERNET PTE. LTD.  TH
64.37.63.18 HostDime.com, Inc. US
106.41.200.151 CHINANET HUNAN PROVINCE NETWORK CN
77.65.212.167 PROGRESO.PL SP Z O.O PL
206.72.194.50 Interserver, Inc US
173.205.127.152 Web Hosting Hub, Inc US
188.241.222.214 Awesome Projects S.R.L. RO
64.40.13.26 GLOBALHOSTINGSOLUTIONS INC US
109.234.166.59 O2SWITCH SAS FR
81.91.85.141 Web4U s.r.o. CZ
172.67.140.248 Cloudflare, Inc. US

Attacking IPs


IP Source (ISP/ASN) Country
103.161.34.10 GSJZ(CHINA)TECHNOLOGY CO.,LIMITED t/a Guosheng IDC lease NL
176.65.131.18 ZeXoTeK IT-Services GmbH NL
176.65.131.19 ZeXoTeK IT-Services GmbH NL
103.161.34.44 GSJZ(CHINA)TECHNOLOGY CO.,LIMITED t/a Guosheng IDC lease NL
103.161.35.72 GSJZ(CHINA)TECHNOLOGY CO.,LIMITED t/a Guosheng IDC lease NL
95.174.113.63 Consumer Internet Cooperative PG-19 RU
204.76.203.84 Intelligence Hosting LLC NL
204.76.203.2 Intelligence Hosting LLC NL
78.41.139.200 HOSTSHIELD LTD NL
45.156.87.223 TechTies Inc. NL
20.198.176.220 Microsoft Corporation SG
45.153.34.104 TechTies Inc. NL
45.153.34.106 TechTies Inc. NL
162.251.238.24 VegasNAP, LLC US
38.45.71.191 Cogent Communications, LLC US
192.129.220.186 RackNerd LLC US
181.214.99.234 Unesty Company DE
162.248.102.46 GALAXYGATE, LLC US
15.204.132.78 OVH SAS US
192.210.181.100 RackNerd LLC US

Malware Hashes

Hash VT Detections Classification
dedb672b0cd94b68c4d232f3ecb90d79 10/60 trojan.agentb/remcos
309e9e9ec97d8c92d8b32fe4418d7ff0 25/55 trojan.mirai/ddos
8bdd2cdd39b2ad7b679faa50f629ce2b 29/62 phishing.akgpp/malurl
3d7bc4241b59780559d21e6433bf9672 29/60 trojan.mirai/miraidlod
5294f25631d20b68ebf3a9acd4cc1f5d 33/64 trojan.malpack/rootkit
d4f0c4ab122e0a7f27ba5864934a4ca8 35/64 trojan.sagnt/r002c0db526
9314f0fa42caebcbbe5261bdd2795f7d 39/61 trojan.tsunami/kaiten
a3d10d1a5be5daa9a42973e54d6c8d0e 39/62 trojan.mirai/usblh926
4ce6a00b6110069929311e18e32973ad 39/63 trojan.tsunami/kaiten
895a8e146f5e855018cb3ce5f85f0e45 41/62 trojan.tsunami/kaiten
e27fb7c5558474234b8a0f884a909ccf 41/63 trojan.mirai/gafgyt
59ce0baba11893f90527fc951ac69912 42/61 trojan.mirai/mozi
cc262c7d2c4f7c23182f33b0b7c38e5a 42/63 trojan.mirai/usblh926
7b61351b598bf22ab0cf7b09a6f89227 44/63 trojan.mirai/gafgyt
dbc520ea1518748fec9fcfcf29755c30 45/62 trojan.mirai/ddos
7822cdf1cf8e30d9997c9743f8897f33 45/64 trojan.tsunami/kaiten
e0c0873263eb23d5092363f938ea9ca2 46/63 trojan.tsunami/kaiten
fbe51695e97a45dc61967dc3241a37dc 47/62 trojan.mirai/mozi
a73ddd6ec22462db955439f665cad4e6 49/62 trojan.mirai/mozi
3849f30b51a5c49e8d1546960cc206c7 50/62 trojan.mirai/mozi

To learn more about how we collect, analyze, and deliver actionable threat intelligence, explore our Threat Intelligence Services. If you’re interested in running your own queries – whether for threat actors, CVEs, infrastructure, or emerging activity – see how our MCP Server helps turn intelligence into practical security insight. Both are designed to support real-world analysis, investigation, and decision-making.

Take advantage of our free threat intel trial.

?

Threat Trends Digest – July 2026

Welcome to the Threat Trends Digest, a monthly view of real-world threat patterns.

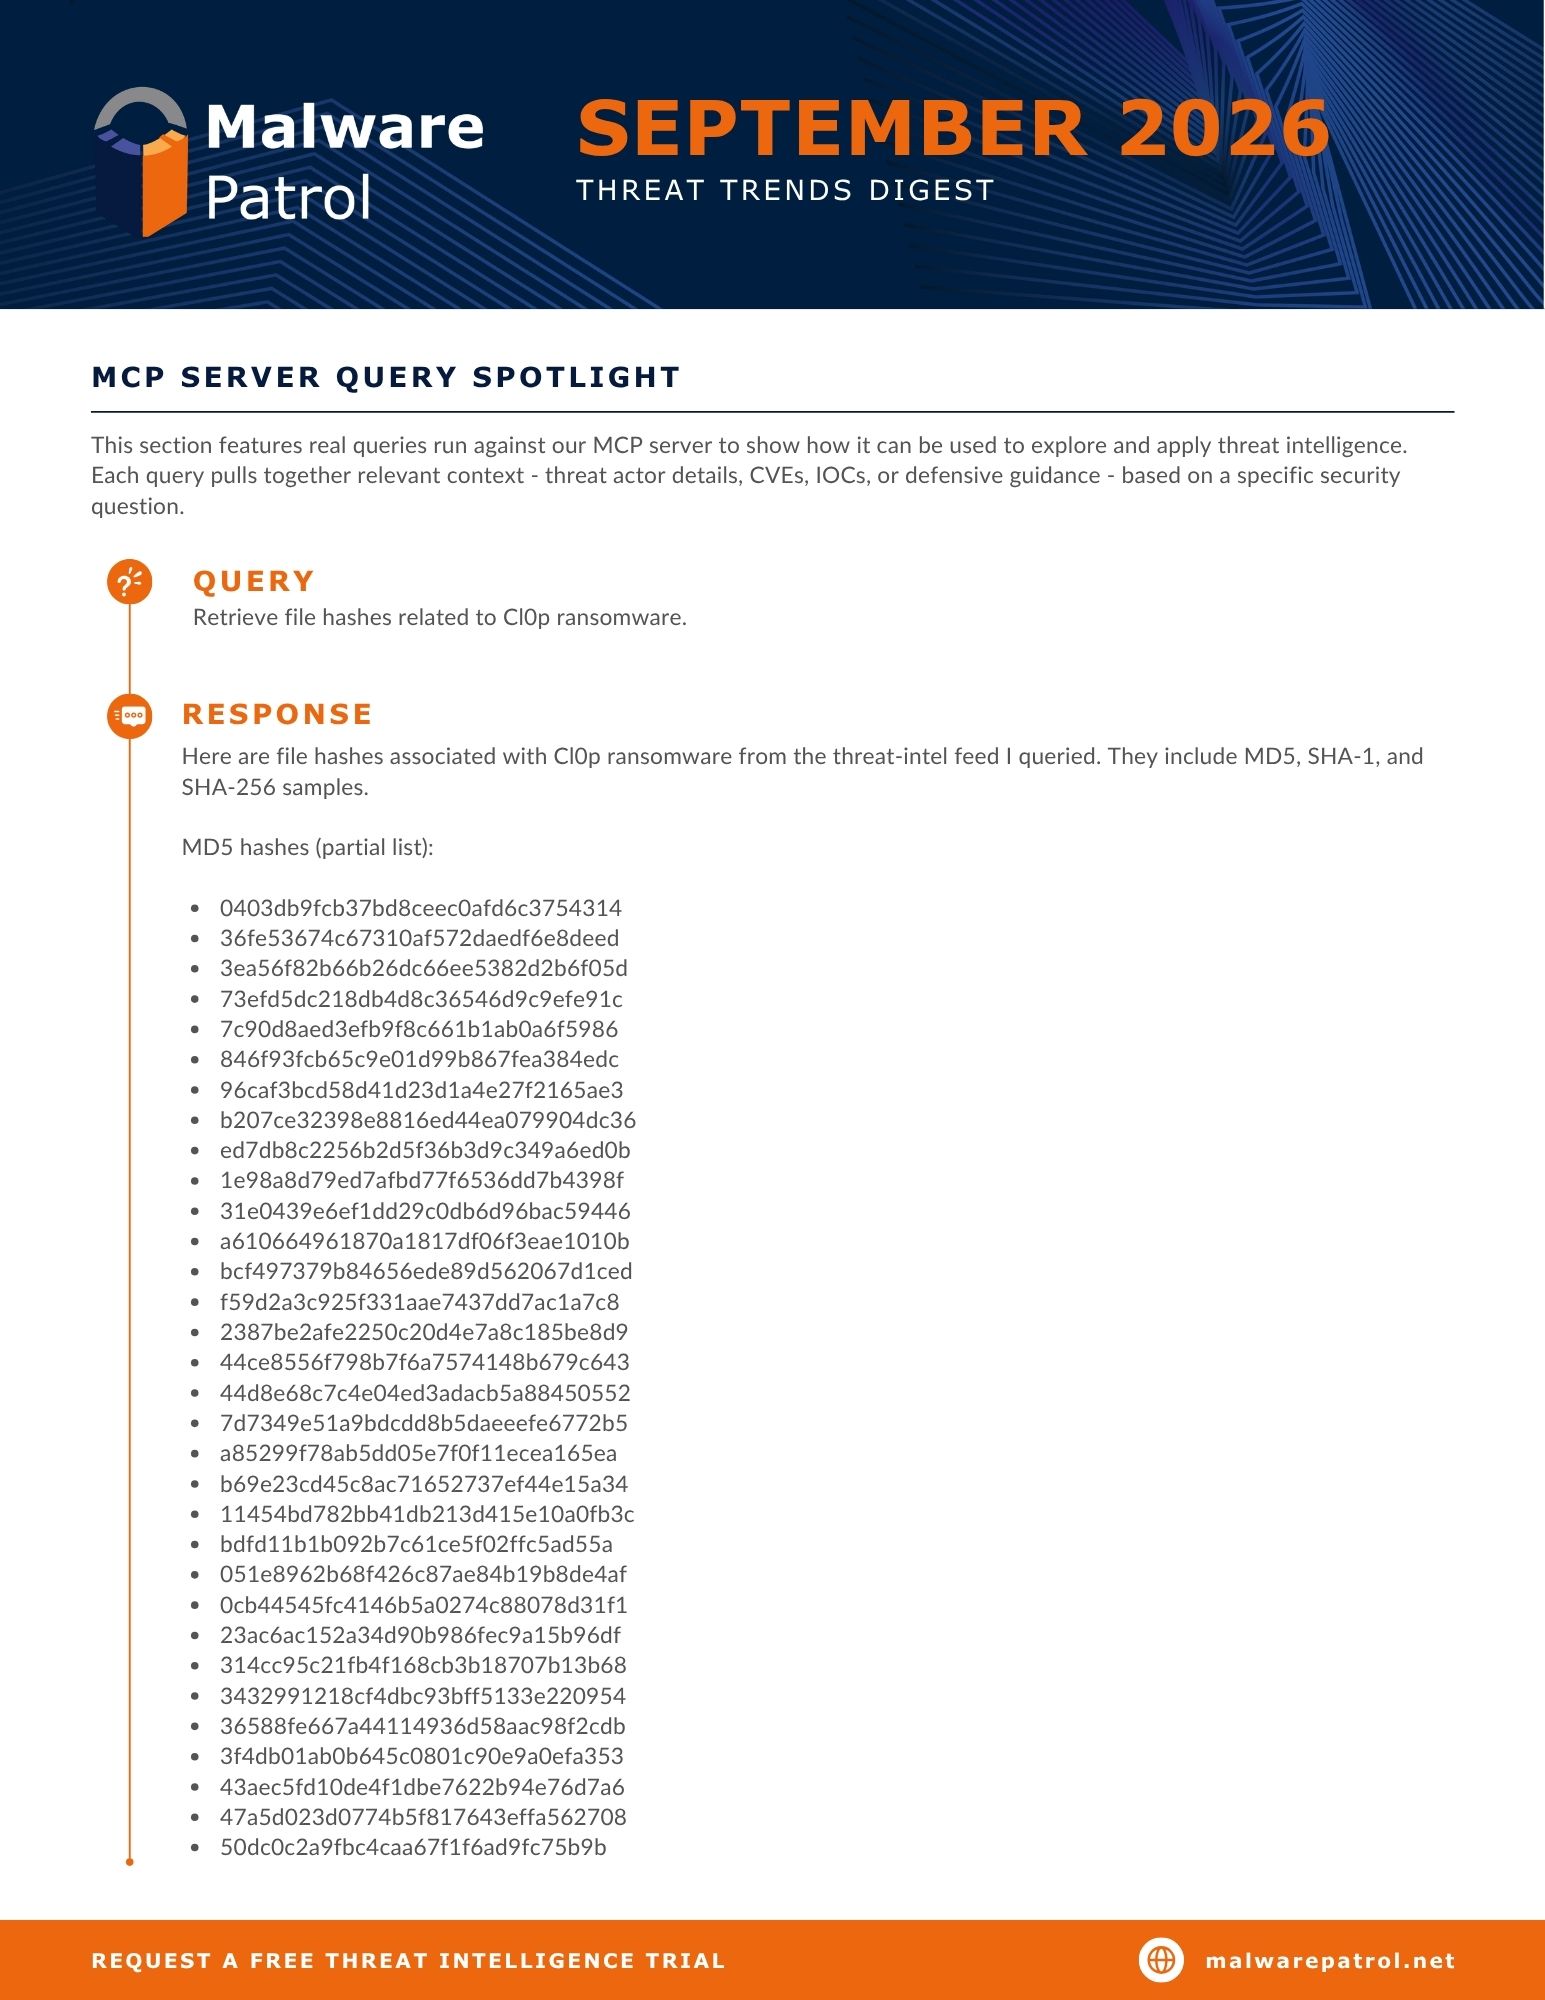
This report compiles data from the previous month using Malware Patrol’s global telemetry and live attack observations to surface key stats on malware, phishing, ransomware, C2s, and domain generation algorithms (DGAs). You’ll find insights into the most exploited TLDs, frequently seen malware hashes and IPs, and other critical indicators. Use this digest to keep a close pulse on attacker behavior, uncover shifting patterns, and better align your defenses with the latest threat activity.

For more articles, check out our #onpatrol4malware blog.
?

IOCs

Malicious IPs

IP Source Country
106.41.200.151 CHINANET HUNAN PROVINCE NETWORK CN
74.115.51.8 Weebly, Inc. US
74.115.51.9 Weebly, Inc. US
213.186.33.19 OVH SAS FR
77.65.212.167 PROGRESO.PL SP Z O.O PL
185.118.115.89 Dream Fusion – IT Services, Lda PT
70.40.210.164 Unified Layer US
27.254.33.92 CSLOXINFO-IDC TH
162.214.80.24 Unified Layer US
62.60.226.198 FEMO IT SOLUTIONS LIMITED DE
51.38.54.48 OVH SAS FR
95.173.180.73 Netinternet Bilisim Teknolojileri AS TR
213.186.33.17 OVH SAS FR
66.116.205.44 P.D.R Solutions FZC IN
213.186.33.87 OVH SAS FR
64.37.63.18 HostDime.com, Inc. US
188.241.222.214 Awesome Projects S.R.L. RO
97.74.93.253 GoDaddy.com, LLC SG
77.75.22.2 SysUP IT GmbH & Co KG AT
51.91.153.81 OVH SAS FR

Attacking IPs

IP Source (ISP/ASN) Country
103.161.34.10 GSJZ(CHINA)TECHNOLOGY CO.,LIMITED t/a Guosheng IDC lease NL
176.65.131.18 ZeXoTeK IT-Services GmbH NL
176.65.131.19 ZeXoTeK IT-Services GmbH NL
103.161.34.44 GSJZ(CHINA)TECHNOLOGY CO.,LIMITED t/a Guosheng IDC lease NL
103.161.35.72 GSJZ(CHINA)TECHNOLOGY CO.,LIMITED t/a Guosheng IDC lease NL
95.174.113.63 Consumer Internet Cooperative PG-19 RU
204.76.203.84 Intelligence Hosting LLC NL
204.76.203.2 Intelligence Hosting LLC NL
78.41.139.200 HOSTSHIELD LTD NL
45.156.87.223 TechTies Inc. NL
20.198.176.220 Microsoft Corporation SG
45.153.34.104 TechTies Inc. NL
45.153.34.106 TechTies Inc. NL
162.251.238.24 VegasNAP, LLC US
38.45.71.191 Cogent Communications, LLC US
192.129.220.186 RackNerd LLC US
181.214.99.234 Unesty Company DE
162.248.102.46 GALAXYGATE, LLC US
15.204.132.78 OVH SAS US
192.210.181.100 RackNerd LLC US

Malware Hashes

Hash (MD5) VT Detections Classification
5dcbf5399e5c9c238a6c467591bd7599 5/60 trojan.encodedpe/msil
471309df0f07c6b122a1715f6f5403ab 6/61 trojan.encodedpe/lausivloader
893a214bc719df8b3141cab10513566a 14/63 adware.polarwind/xzzmo
2b54972e8a3fc86e480c95aacd80ae9a 14/61 fragtor
8bdd2cdd39b2ad7b679faa50f629ce2b 29/62 phishing.akgpp/malurl
1f20cc44056395c837cf9a7211b09c04 29/63 trojan.usblgq26/abmrisk
246ff7da8826a2cab11f5013000b0b83 35/64 trojan.gelesz/runner
9256ec6a350db5344bad23866fe2c1e9 41/66 trojan.geluasz/usblev26
59ce0baba11893f90527fc951ac69912 42/61 trojan.mirai/mozi
b24c8affd984bc47b7a6c5bd11e58b16 43/63 trojan.tsunami/kaiten
dbc520ea1518748fec9fcfcf29755c30 45/62 trojan.mirai/ddos
fbe51695e97a45dc61967dc3241a37dc 47/62 trojan.mirai/mozi
c0fd19c0e4a252efb1864b267fb154ae 53/70 adware.ababsoftware/downloadasist
a73ddd6ec22462db955439f665cad4e6 49/62 trojan.mirai/mozi
796c596185e63803a4ec4003aa60f425 54/68 adware.qjwmonkey/bundler
3849f30b51a5c49e8d1546960cc206c7 50/62 trojan.mirai/mozi
5dfc3eefe1c51312d0020910020c4025 55/67 adware.qjwmonkey/nezchi
31549917cdc6e3f9d40a48ea5998493f 56/67 adware.qjwmonkey/dangeroussig
eec5c6c219535fba3a0492ea8118b397 53/63 trojan.mirai/mozi
96dd80012c33291e1621b66f5bd66967 61/69 adware.qjwmonkey/bundler

To learn more about how we collect, analyze, and deliver actionable threat intelligence, explore our Threat Intelligence Services. If you’re interested in running your own queries – whether for threat actors, CVEs, infrastructure, or emerging activity – see how our MCP Server helps turn intelligence into practical security insight. Both are designed to support real-world analysis, investigation, and decision-making.

Take advantage of our free threat intel trial.

?

Threat Trends Digest – June 2026

?

Welcome to the Threat Trends Digest, a monthly view of real-world threat patterns.

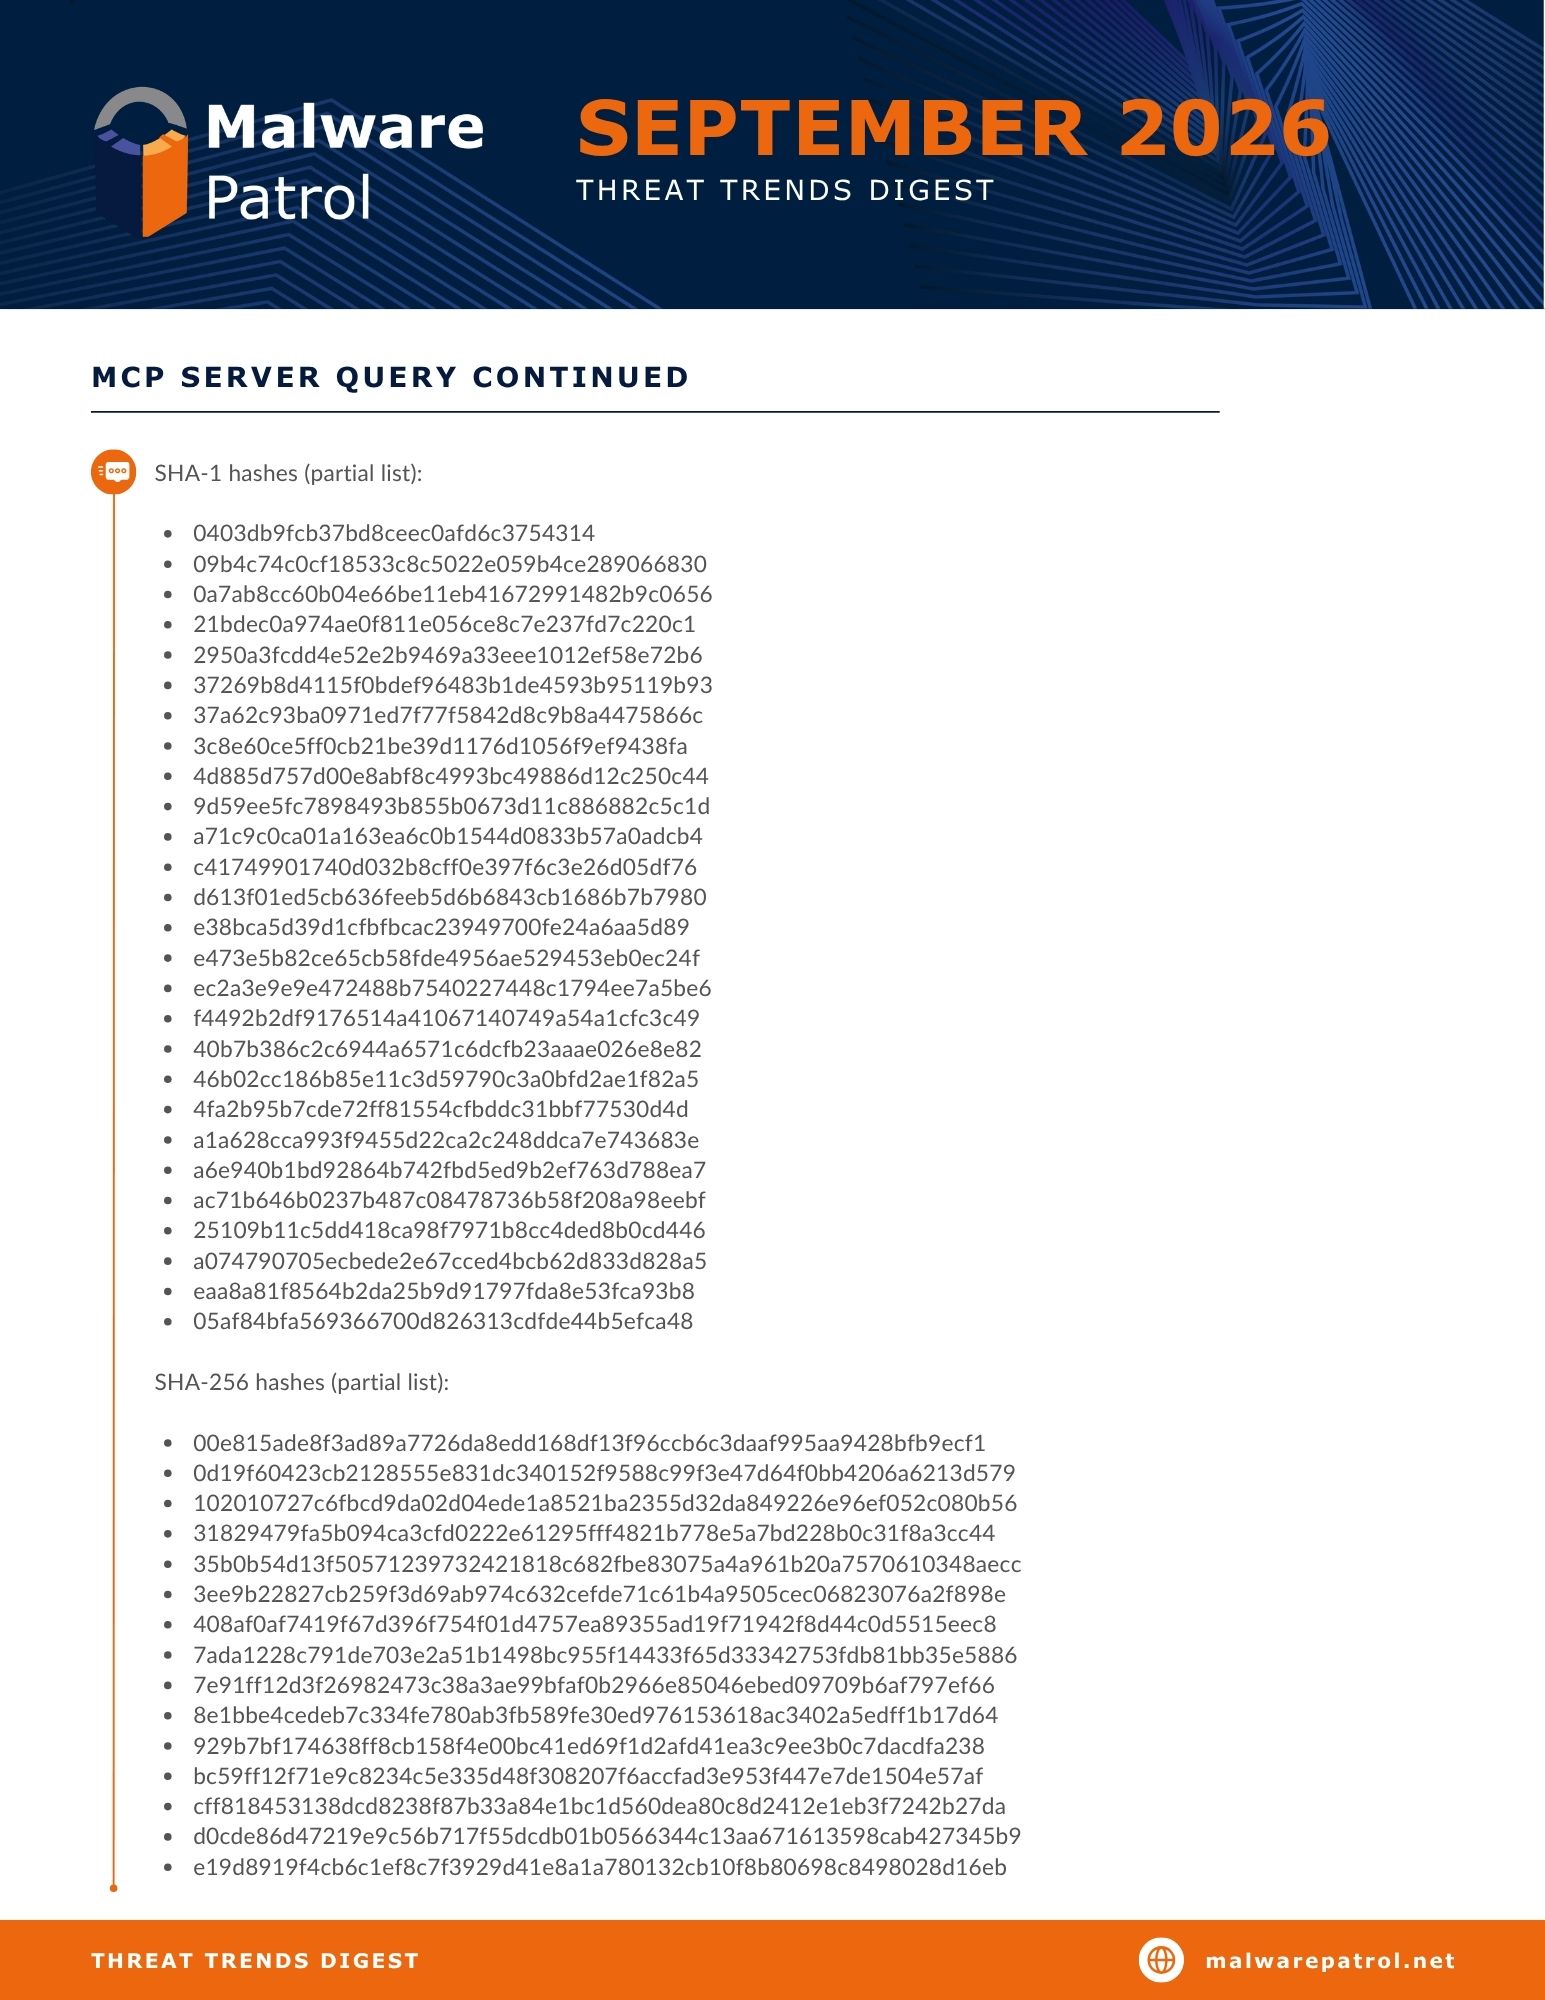
This report compiles data from the previous month using Malware Patrol’s global telemetry and live attack observations to surface key stats on malware, phishing, ransomware, C2s, and domain generation algorithms (DGAs). You’ll find insights into the most exploited TLDs, frequently seen malware hashes and IPs, and other critical indicators. Use this digest to keep a close pulse on attacker behavior, uncover shifting patterns, and better align your defenses with the latest threat activity.

For more articles, check out our #onpatrol4malware blog.
??

IOCs

Malicious IPs

IP Source (ISP) Country
213.186.33.87 OVH SAS FR
43.242.37.17 YOTTA NETWORK SERVICES PRIVATE LIMITED IN
188.241.222.214 Awesome Projects S.R.L. RO
96.125.172.210 Network Solutions, LLC US
109.234.166.59 O2SWITCH SAS FR
70.40.210.164 Unified Layer US
64.37.63.18 HostDime.com, Inc. US
154.0.169.106 AFRIHOST SP (PTY) LTD ZA
185.118.115.89 Dream Fusion – IT Services, Lda PT
213.186.33.19 OVH SAS FR
213.186.33.4 OVH SAS FR
104.21.89.111 Cloudflare, Inc. US
74.115.51.9 Weebly, Inc. US
77.65.212.167 PROGRESO.PL SP Z O.O PL
64.40.13.26 GLOBALHOSTINGSOLUTIONS INC US
106.41.200.151 CHINANET HUNAN PROVINCE NETWORK CN
185.199.110.133 GitHub, Inc. US
185.199.109.133 GitHub, Inc. US
185.199.108.133 GitHub, Inc. US
185.199.111.133 GitHub, Inc. US

Attacking IPs

IP Source (ISP/ASN) Country
213.199.50.203 Contabo GmbH FR
167.86.103.106 Contabo GmbH FR
78.41.139.200 HOSTSHIELD LTD NL
167.86.95.106 Contabo GmbH FR
207.180.236.132 Contabo GmbH FR
38.242.151.30 Contabo GmbH FR
213.199.49.171 Contabo GmbH FR
161.97.91.253 Contabo GmbH FR
213.199.49.105 Contabo GmbH FR
173.212.226.152 Contabo GmbH FR
161.97.92.64 Contabo GmbH FR
161.97.91.150 Contabo GmbH FR
84.247.184.190 Contabo GmbH FR
84.247.185.83 Contabo GmbH FR
80.75.212.112 Ferdinand Zink trading as Tube-Hosting DE
103.161.34.44 GSJZ(CHINA)TECHNOLOGY CO.,LIMITED t/a Guosheng IDC lease NL
176.65.131.19 ZeXoTeK IT-Services GmbH NL
130.12.183.13 Netiface LLC DE
176.65.131.18 ZeXoTeK IT-Services GmbH NL
103.161.34.10 GSJZ(CHINA)TECHNOLOGY CO.,LIMITED t/a Guosheng IDC lease NL

Malware Hashes

Hash VirusTotal Detections VirusTotal Label
31549917cdc6e3f9d40a48ea5998493f 56/67 adware.qjwmonkey/dangeroussig
8bdd2cdd39b2ad7b679faa50f629ce2b 29/62 phishing.akgpp/malurl
59ce0baba11893f90527fc951ac69912 42/61 trojan.mirai/mozi
3849f30b51a5c49e8d1546960cc206c7 50/62 trojan.mirai/mozi
eec5c6c219535fba3a0492ea8118b397 53/63 trojan.mirai/mozi
a73ddd6ec22462db955439f665cad4e6 49/62 trojan.mirai/mozi
796c596185e63803a4ec4003aa60f425 54/68 adware.qjwmonkey/bundler
c0fd19c0e4a252efb1864b267fb154ae 53/70 adware.ababsoftware/downloadasist
96dd80012c33291e1621b66f5bd66967 61/69 adware.qjwmonkey/bundler
fbe51695e97a45dc61967dc3241a37dc 47/62 trojan.mirai/mozi
724f25e7f93eae0ae54a80142e11b7ef 38/62 trojan.sshdoor/abtrojan
4cbfce17e2733c3926997aab98c20b8f 27/60 trojan.grhe/msil
5377e8f2ebdb280216c37a6195da9d6c 47/62 trojan.hajime/mirai
cb7569803c981f18d9e0756f0032b81d 11/60 trojan.agentb/remcos
936b35bfee8232f437bf6b46e88401dd 39/61 trojan.sshdoor/sshdkit
c3f53808a624b526d51356430923f9c6 4/61 trojan.encodedpe/packed2
dbc520ea1518748fec9fcfcf29755c30 45/62 trojan.mirai/ddos
f7459bc26baf2db287c39770f6a1e19c 35/63 trojan.mirai/awtg
9b6c3518a91d23ed77504b5416bfb5b3 49/63 trojan.hajime/mirai
b5b87f87c084115b7a57898dc54a6888 20/60 trojan.grhd/msil

To learn more about how we collect, analyze, and deliver actionable threat intelligence, explore our Threat Intelligence Services. If you’re interested in running your own queries – whether for threat actors, CVEs, infrastructure, or emerging activity – see how our MCP Server helps turn intelligence into practical security insight. Both are designed to support real-world analysis, investigation, and decision-making.
Take advantage of our free threat intel trial.

?

FIFA World Cup 2026: Emerging Domain Activity

FIFA World Cup 2026 cyber threats blog post header image

FIFA World Cup 2026 Cyber Threats

Major sporting events have long attracted cybercriminal activity, and the 2026 FIFA World Cup is no exception. Throughout the lead-up to the tournament, we have observed a growing number of FIFA- and World Cup-themed domains associated with betting operations, fake streaming services and apps, credential theft, and other forms of brand abuse. Public reporting has likewise documented concerns around ticket and merchandise scams, fraudulent hospitality offers, and phishing campaigns targeting fans and travelers.

The domains highlighted in this research were identified through our Emergent Threats feed, which aggregates intelligence from multiple sources, including newly registered domains, newly observed domains, certificate issuance activity, and other early-warning indicators. This allows defenders to identify potentially malicious infrastructure as it emerges, often before it becomes widely recognized or actively weaponized.

With the tournament soon underway, organizations should expect continued abuse of FIFA branding and related event infrastructure. Security teams should monitor for World Cup-themed domains, particularly those leveraging ticketing, hospitality, streaming, betting, and account-related lures.

Official FIFA World Cup Infrastructure

One of the simplest ways to reduce risk is to maintain an allowlist of known legitimate FIFA and World Cup-related infrastructure. While organizations should always validate domains independently and avoid overly broad allowlisting practices, the domains below represent official FIFA properties, tournament resources, hospitality platforms, and host-city websites associated with the 2026 FIFA World Cup.

These domains can serve as a useful baseline when reviewing newly registered domains, investigating user reports, tuning detections, or identifying suspicious lookalike registrations. Domains that closely mimic these properties, particularly those containing terms such as “official,” “tickets,” “hospitality,” “login,” “vip,” or host-city names, should be reviewed carefully for potential phishing, fraud, or brand-abuse activity.

FIFA

  • fifa.com
  • www.fifa.com

Official World Cup Pages

  • fifa.com/en/tournaments/mens/worldcup/canadamexicousa2026
  • fifa.com/en/tournaments/mens/worldcup
  • fifa.com/tickets
  • fifa.com/en/tournaments/mens/worldcup/canadamexicousa2026/articles/resale-ticket-exchange-marketplace (Ticket Resale/Exchange Marketplace)
  • fifa.com/hospitality

Host Cities

  • atlantafwc26.com
  • bostonfwc26.com
  • dallasfwc26.com
  • houstonfwc26.com
  • kansascityfwc26.com
  • losangelesfwc26.com
  • miamifwc26.com
  • nynjfwc26.com
  • philadelphiasoccer2026.com
  • bayareahostcommittee.com
  • seattlefwc26.org
  • vancouverfwc26.ca
  • torontofwc26.ca

Hospitality

  • fifaworldcup26.suites.fifa.com


What We’re Seeing 

Analysis of FIFA World Cup 2026 cyber threats using domain data reveals several recurring categories:

  • Betting and gambling sites using FIFA and World Cup branding to promote sportsbooks, casinos, odds platforms, and wagering services.
  • Credential theft and phishing portals incorporating keywords such as “login,” “register,” “official,” and “account.”
  • Fake streaming and live broadcast sites leveraging terms such as “tv,” “live,” “zhibo,” and “kanqiu.”
  • General FIFA brand abuse designed to capture search traffic, impersonate official services, or redirect users to unrelated content.

Common Domain Patterns

Many suspicious domains appear to be generated from templates, combining FIFA-related keywords with generic modifiers, geographic identifiers, betting terms, or randomly generated strings.

Examples include:

fifa + worldcup + tickets
fifa + official + login
fifa + live + tv
fifa + 2026 + bet
fifa + host city + hotels

Security teams should also watch for clusters of similarly named domains, sequential registrations, domains hosted on free platforms such as Pages.dev, and domains combining FIFA branding with local language terms for betting, streaming, or sports content.

Useful hunting patterns for newly registered and newly observed domains can be found below in the Hunting/Regex section.

Download the Dataset

To assist defenders, we analyzed and categorized thousands of FIFA- and World Cup-themed domains identified through our Emergent Threats feed. Unlike traditional newly registered domain datasets, this feed combines multiple early-warning sources, including newly registered domains, newly observed domains, certificate issuance activity, and other indicators of emerging infrastructure.

The resulting data includes domains categorized as betting, streaming, phishing risk, Club World Cup, and general World Cup brand abuse. Organizations can use this data as a practical starting point for detection engineering, threat hunting, enrichment, and proactive monitoring.

Through August 15th, 2026 you can download the categorized domain list here.


Hunting/Regex

General
(?i)(?=.*(fifa|worldcup|world-cup|fwc26|fifawc|wc2026|copa[-_.]?mundial|mundial2026|shijiebei))(?=.*(ticket|tickets|hospitality|vip|login|register|official|tv|live|stream|bet|odds|casino|slot|togel|apk|download|hotel|travel|boletos|entradas|zhibo|kanqiu|h5|wap|app))
False Positive Suppression
(?i)(afifa|khafifa|hafifa|amalfifa|fifabric|fifamily|fifashion|defifa|fifarm|hififa|ififa)
Core FIFA / World Cup seed terms
(?i)(^|[-_.])(fifa|fwc26|fifawc|fifawcup|wc2026|worldcup|world-cup|fifaworldcup)([-_.]|$)
FIFA + 2026 permutations
(?i)(fifa[-_.]?(2026|26)|(2026|26)[-_.]?fifa|fwc[-_.]?26|wc[-_.]?2026)
World Cup 2026 permutations
(?i)(world[-_.]?cup[-_.]?(2026|26)|(2026|26)[-_.]?world[-_.]?cup|fifa[-_.]?world[-_.]?cup[-_.]?(2026|26))
Fake official / portal lures
(?i)(fifa|worldcup|fwc26|wc2026).*(official|offical|portal|account|login|signin|register|verify|auth|admin|secure|access)
Ticketing / hospitality / travel
(?i)(fifa|worldcup|fwc26|wc2026).*(ticket|tickets|resale|refund|hospitality|vip|suite|pass|entry|hotel|hotels|lodging|apartment|travel|parking|transport|limo)
Streaming / live scores
(?i)(fifa|worldcup|fwc26|wc2026).*(tv|live|stream|streaming|watch|broadcast|score|scores|schedule|fixture|match|zhibo|kanqiu|tiyu|shijiebei)
Betting / gambling
(?i)(fifa|worldcup|fwc26|wc2026).*(bet|odds|casino|slot|slots|togel|poker|stake|parlay|jackpot|gacor|bola|cuan|rtp|sbobet)
APK / game download lures
(?i)(fifa|worldcup).*(apk|android|download|mobile|app|mod|hack|coin|coins|generator|ultimate[-_.]?team|ppsspp)
Cloudflare Pages / disposable hosting
(?i)^(?=.*(fifa|worldcup|fwc26|wc2026)).*\.pages\.dev$
(?i)(fifa|worldcup|fwc26|wc2026).*\.workers\.dev$
Host-city abuse
(?i)(fifa|worldcup|fwc26|wc2026).*(atlanta|boston|dallas|houston|kansas[-_.]?city|los[-_.]?angeles|miami|new[-_.]?york|nyc|new[-_.]?jersey|philadelphia|philly|seattle|vancouver|toronto|guadalajara|monterrey|mexico[-_.]?city|cdmx)
Spanish/Mexico-focused terms
(?i)(fifa|worldcup|mundial|copa[-_.]?mundial).*(boleto|boletos|entrada|entradas|hotel|viaje|vip|transmision|en[-_.]?vivo|apuesta|apuestas)
Chinese-language targeting
(?i)(fifa|worldcup|shijiebei|???).*(zhibo|kanqiu|tiyu|saicheng|yuce|jingcai|touzhu|maiqiu|zh|zhcn|zhs|h5|wap)
High-volume generated campaign pattern
(?i)^(cn|ch|hk|jp|kr|th|us|global|intl|official|m|h5|wap|web|app|live|tv|score|login|register)[-_.].*(fifa|worldcup|fifawc|cwcfifa|wc2026)
Numbered / template-generated domains
(?i)(fifa|worldcup|fwc26|wc2026).*[0-9]{2,4}
(?i)(fifa|worldcup|fwc26|wc2026).*(88|888|999|234|777|138|168|303|365|789)
Club World Cup overlap
(?i)(fifa|cwc|club[-_.]?world[-_.]?cup|fcwc).*(2025|2026|ticket|tv|live|bet|official|app|login)
“Official” Impersonation Cluster
(?i)(official|offical|auth|verify|portal|secure|account|login).*(fifa|worldcup)
H5 / WAP Pattern
This is extremely common in Asian-focused campaigns.
(?i)(^h5-|^wap-|^m-|mobile|app).*(fifa|worldcup)
Country/Language Prefix Campaigns
(?i)^(cn|ch|hk|jp|kr|th|tw|vn|sg|id)[-_.]
combined with:
(?i)(fifa|worldcup|fifawc|wc2026)
Number-Based Gambling Naming
(?i)(fifa|worldcup).*(88|888|168|365|777|789|123|138|303)
High-Abuse TLDs
.cfd
.click
.xyz
.pw
.cam
.fun
.space
.shop

Free subdomain providers
(?i)(fifa|worldcup).*\.(uk|us|sa|za|ru)\.com$

?

How big are your threat data gaps?

See for yourself.

?